General importance of information security
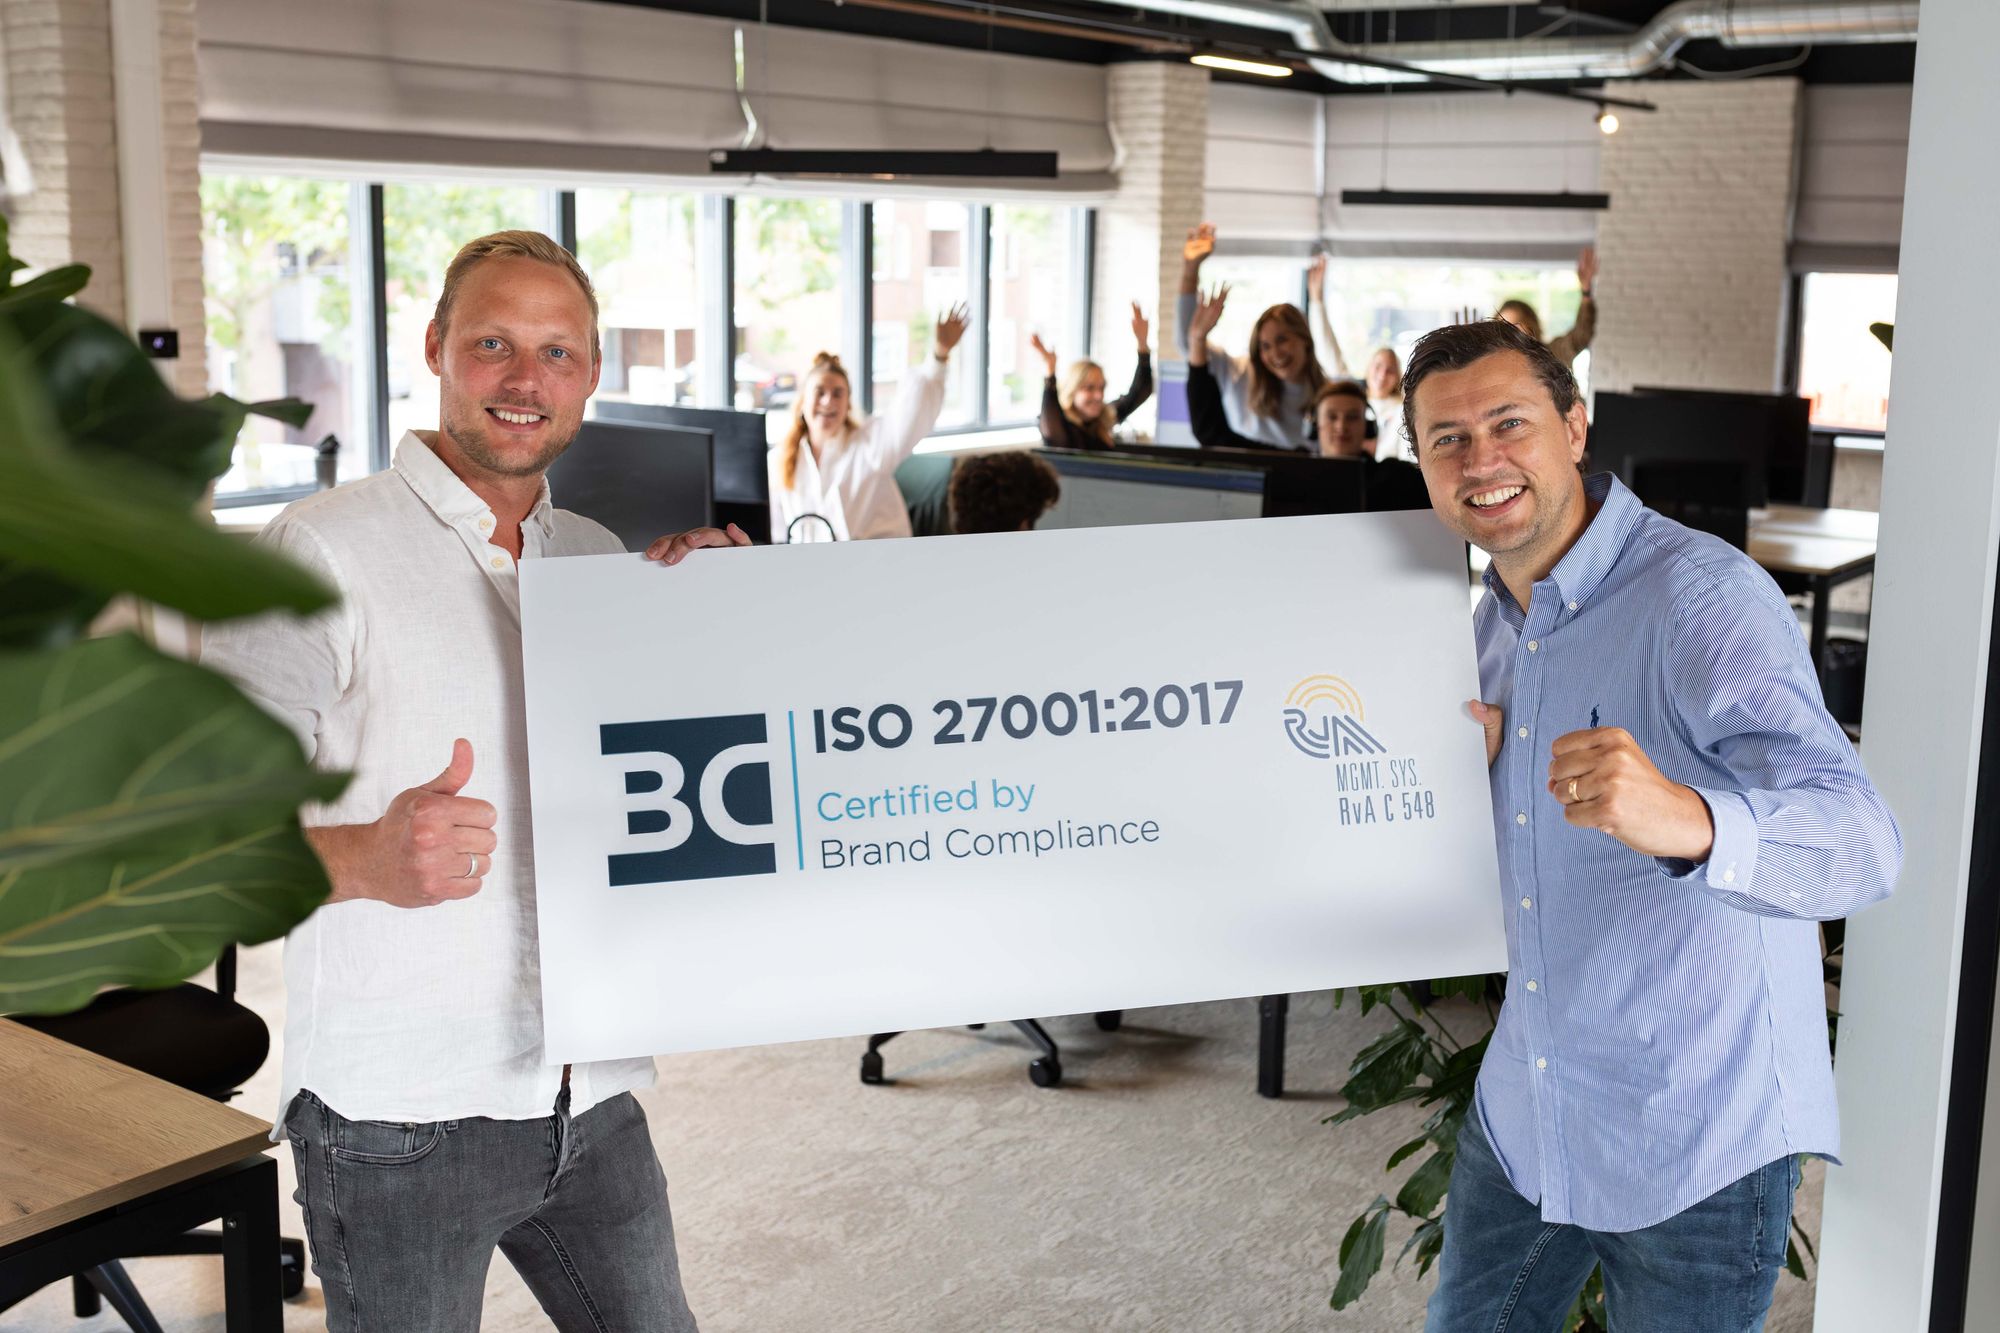
Jeroen, co-founder at vPlan, says: "Of course we were already working safely, but now we can also prove it. This also improves our market position, because more and more companies are checking whether a company is ISO-certified before they do business with it. So ISO is increasingly a requirement. With such certification, we can therefore reassure (potential) customers, as it were, that things are fine with us."
What is ISO?
The abbreviation ISO means International Organization for Standardization. This organization is responsible for creating, managing and improving standards for organizations, processes and inspections. Think 9001 for quality management or 27001 for information security, for example. "With an ISO 27001 certificate, you can demonstrate that your organization is able to manage, evaluate and improve processes around information security," explains Rick Tuk, Security Officer at vPlan.
When an organization is ISO certified, this means that it meets all the requirements of the relevant international standard. An independent external organization assesses this based on research. This investigation is also called an (external) audit.
How does an ISO audit work?
Rick: "You don't get ISO certification overnight; it takes months of work. At vPlan we started with a baseline measurement, or a gap audit, performed by Dionach. "During such an audit it is examined to what extent an organization already complies with the standard and where additional attention should be given. Based on this, we expanded and optimized our management system. We then had an internal audit performed by Dionach to see where we stand. An internal audit is a mandatory, annual part of certification. This showed that we could go up for certification."
He continues, "The certification audit consists of two phases and is conducted by an independent certification body, in our case this was Brand Compliance. Phase 1 assesses the readiness of our organization based on documentation and knowledge for phase 2. In phase 2, a 3-day audit was conducted at our office. During these intensive days, the implementation and effectiveness of the management system is assessed. A report is then prepared. vPlan fortunately passed with flying colors and was thus nominated by the auditor for certification."
What does it mean for our clients and partners?
Our clients can be assured that we at vPlan always handle information with awareness. In addition, we continually strive for improvement and professionalization within the organization. With us, you can be sure that we have our affairs in order:
- We handle information consciously and securely;
- We have insight into the processes surrounding information security;
- We put the information security of our customers first.
As a result of this article, do you have any questions about ISO at vPlan? If so, feel free to contact us, we would be happy to answer your questions!

Work at vPlan
We are looking for new colleagues.